Ephemeral messaging fundamentally transformed how we share casual moments. When mainstream apps introduced "View Once" photos and self-destructing audio, it addressed a critical human desire: sharing something sensitive without leaving an indelible digital footprint. However, for professionals, engineers, legal advisors, and privacy-conscious teams, conventional chat apps present severe vulnerabilities: mandatory mobile number linking, cloud chat backups, screenshot loopholes, and centralized corporate metadata tracking.
1. The Problem with Centralized Ephemeral Chat Apps
While WhatsApp and similar platforms popularized "View Once" media, they operate within a walled-garden ecosystem tied to personal phone numbers and corporate identity graphs. When you share a confidential contract, credentials, or sensitive media over standard messaging apps:
- Account & Phone Number Exposure: Both parties must share their personal identities, exposing contact details and presence status.
- Cloud Backup Leakage: Even if a message is set to disappear, device backups (iCloud / Google Drive) often store decrypted cached media or notification logs.
- Corporate Server Logging: Message routing metadata, connection IP addresses, timestamps, and recipient relationships remain logged on central messaging servers indefinitely.
- Platform Incompatibility: You cannot securely send a one-time secret to an external vendor, client, or team member who doesn't use the same proprietary mobile application.
View Once solves this through browser-native zero-knowledge cryptography. Anyone with a modern web browser on Android, iOS, Windows, Mac, or Linux can receive and decrypt ephemeral media with absolute cryptographic certainty.
2. The Modern View Once Experience: Full Multimedia Sharing
The latest major release of View Once introduces capabilities that bridge the gap between instant messaging fluidity and military-grade encryption standards:
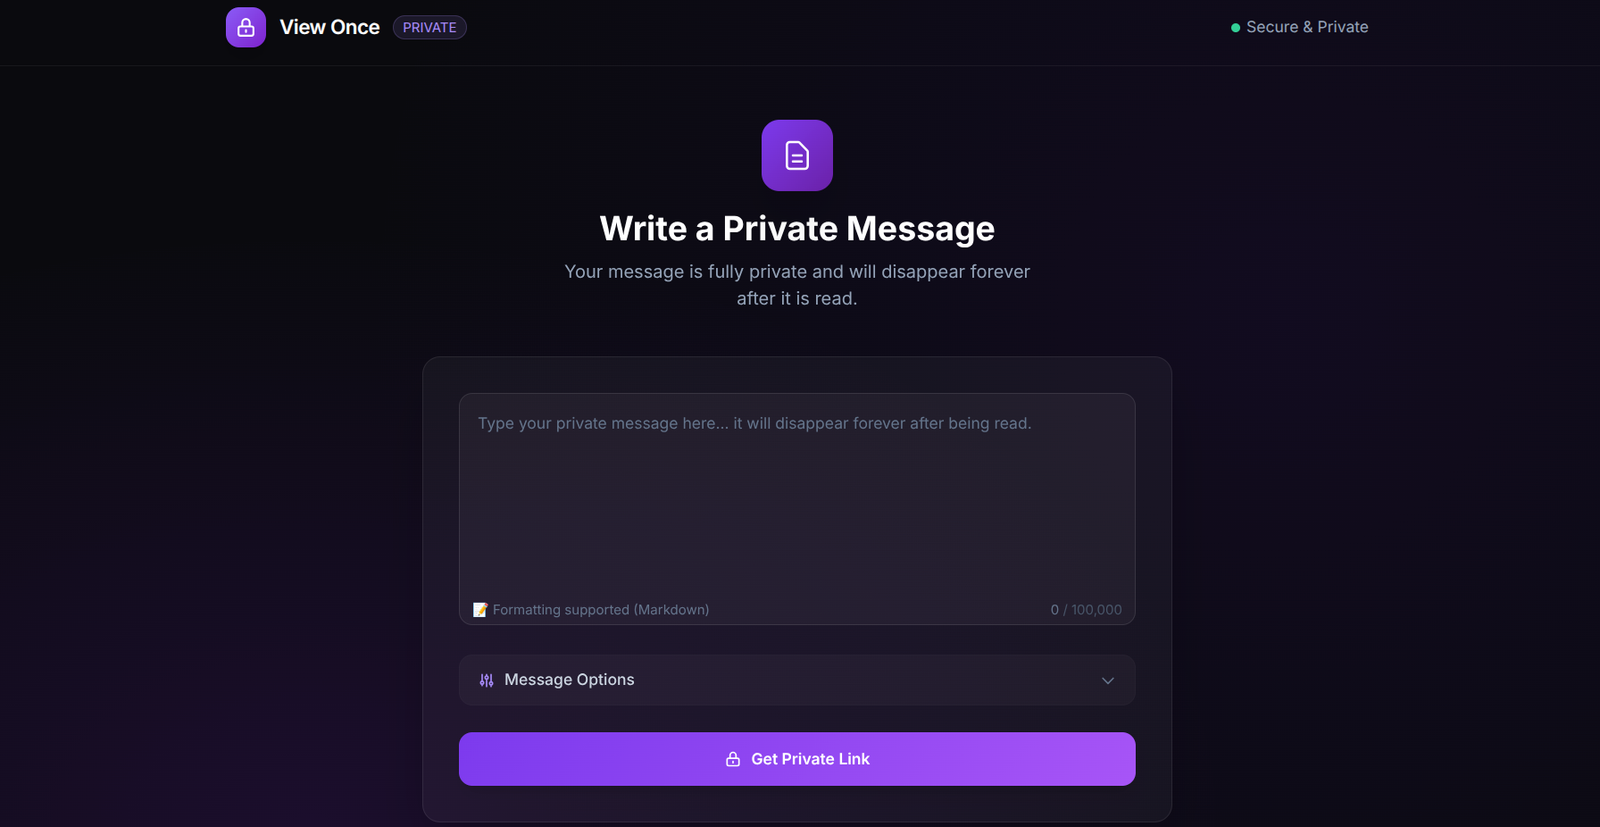
HD vs. Standard Image Sharing (With Zero EXIF Footprint)
When sending photos through standard messengers, aggressive compression algorithms often blur vital details on contracts, architectural blueprints, or credential cards. Alternatively, uncompressed transfers frequently leak confidential EXIF metadata (exact GPS coordinates, camera serial numbers, and capture timestamps).
View Once introduces dual-mode image encryption:
- Standard Optimized Mode: Automatically compresses images client-side within an HTML5 Canvas, generating an ultra-lightweight encrypted payload ideal for fast cellular loading.
- Full HD Lossless Mode: Preserves 100% pixel-perfect clarity for high-resolution diagrams, complex technical schematics, identity proofs, and design drafts.
- Autonomous EXIF Sanitization: Before encryption occurs in browser memory, all embedded location tags, device signatures, and hardware timestamps are stripped clean, preventing accidental metadata leaks.
Encrypted In-Browser Video Streaming
Sharing confidential video recordings — such as internal bug reproductions, executive briefing clips, or private KYC video verifications — traditionally required uploading to cloud storage services like Google Drive or Dropbox, creating persistent links that linger forever.
View Once allows users to attach video files directly. The video is chunked and encrypted into binary ArrayBuffers using AES-256-GCM before upload. When the recipient opens the link, the video streams and decrypts entirely in volatile RAM. The moment the tab is closed or the destruction trigger fires, the video buffer is instantly garbage-collected and permanently erased from the hosting server.
Universal Document & File Attachments
Beyond photos and video, View Once supports any file format up to 25MB — including confidential PDF contracts, financial Excel spreadsheets, compressed ZIP archives, and private SSL/SSH certificates. The file bytes are treated as raw cryptographic payloads, completely opaque to our servers, and auto-destructed upon delivery.
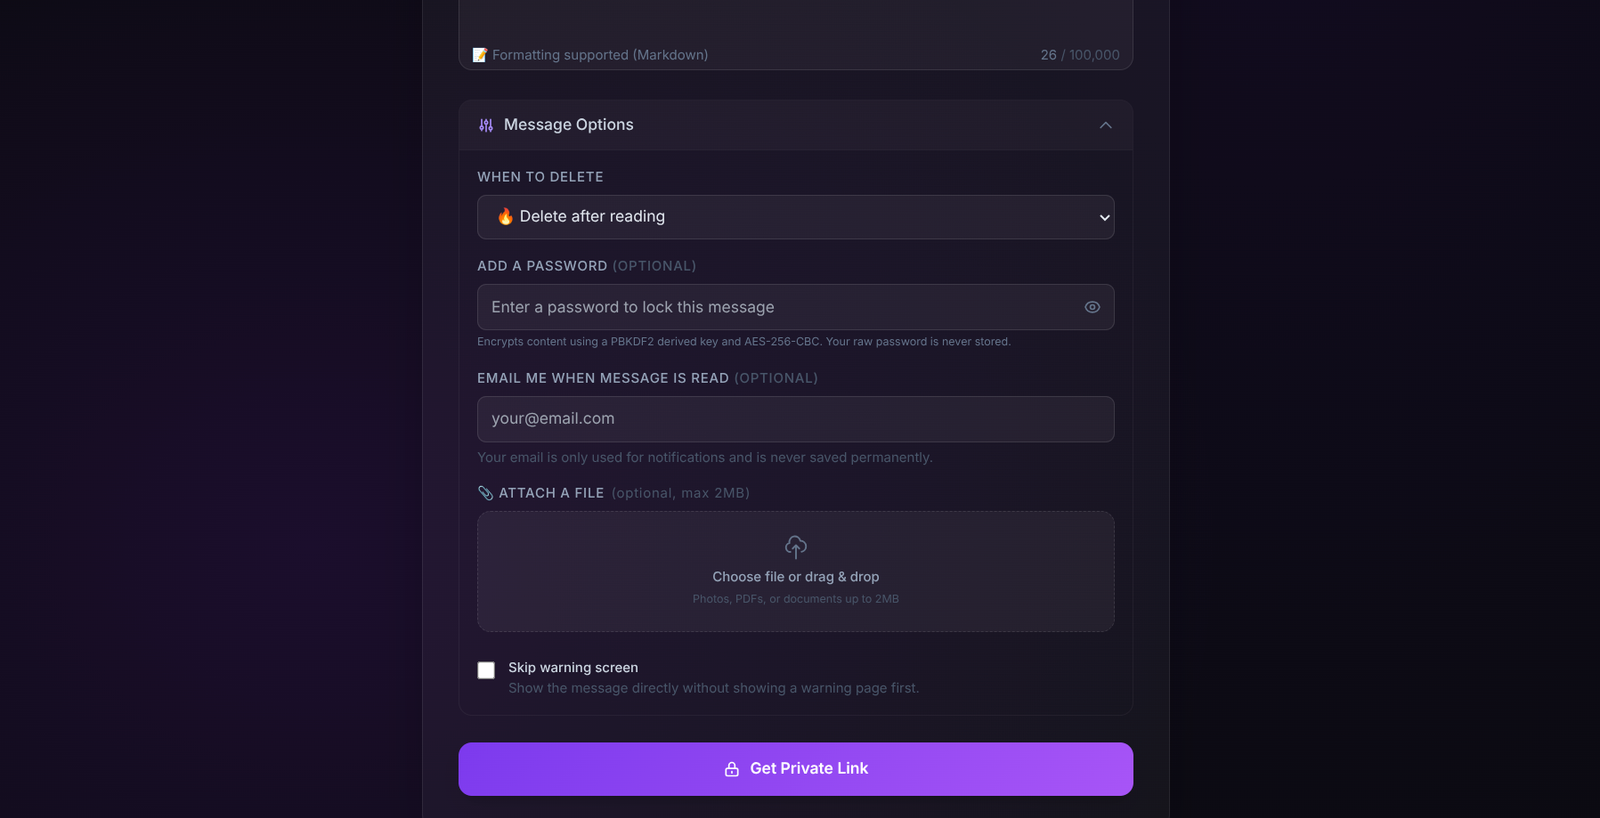
3. Granular Control Over Self-Destruction & Security
Every piece of shared media or text comes with customizable operational governance:
- Destruction Triggers: Choose between immediate destruction (Burn after reading), timed expiration (1 hour, 24 hours, 7 days), or manual burn.
- Optional Decryption Passphrase: Add a secondary layer of security by requiring a shared secret passphrase. The key is hardened using PBKDF2 with over 100,000 iterations, shielding the message against brute-force attacks.
- Discreet Reference Tags: Label secrets with custom names (e.g.,
Client_NDA_v2) so you can track multiple dispatches without compromising secret content. - Email Read Receipts: Receive an automated notification the exact second your link is opened and incinerated.
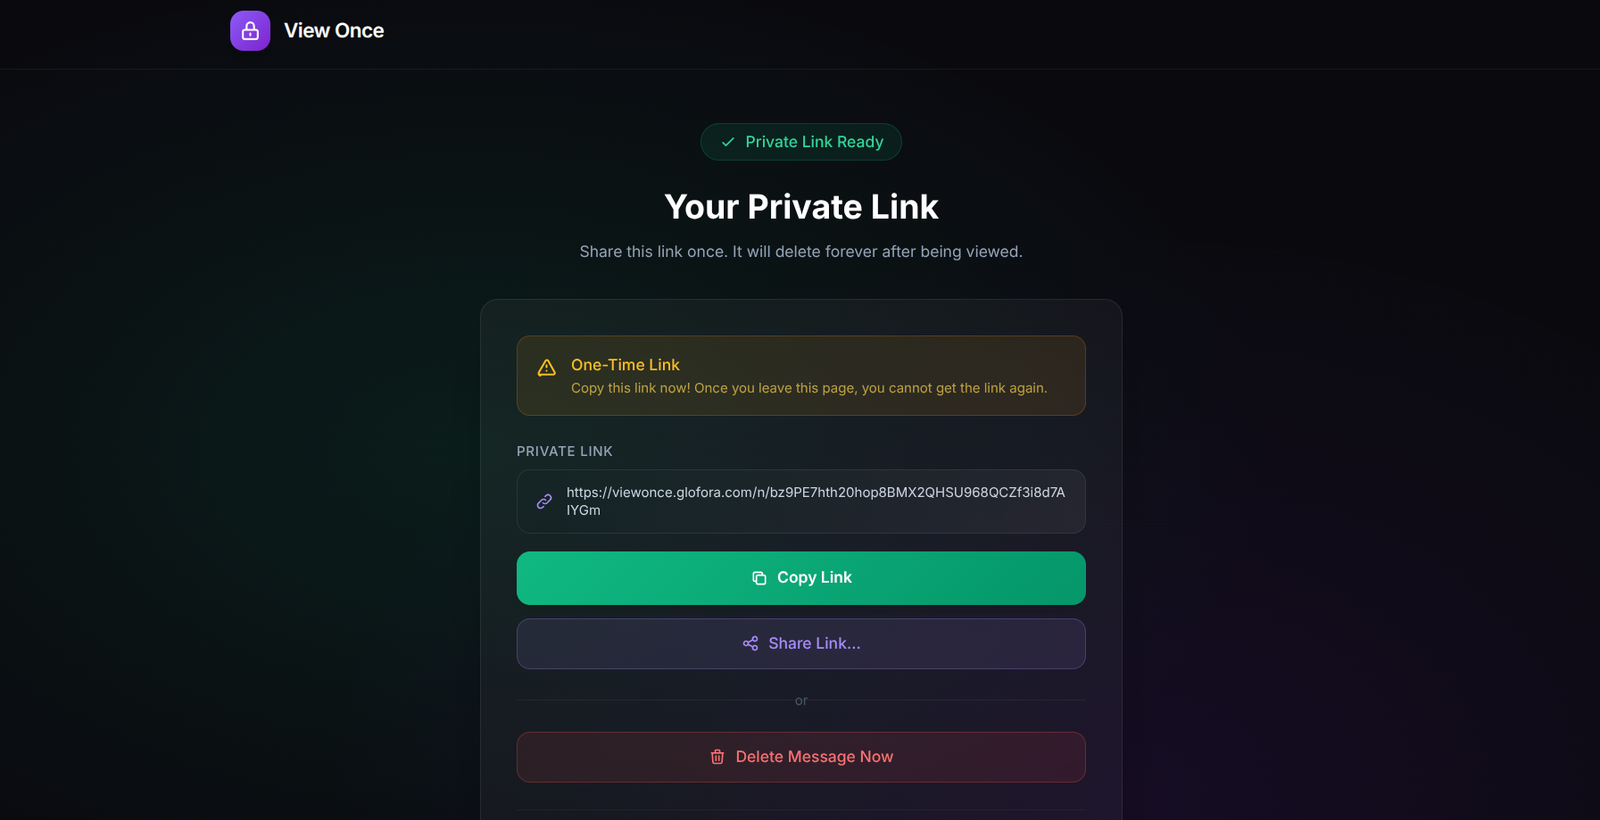
4. The Zero-Knowledge URL Hash Architecture
How can View Once guarantee that even Glofora's server infrastructure cannot read your messages, photos, or videos? The secret lies in the URL Anchor Fragment (#).
According to the RFC 3986 Internet Standard, everything following the # character in a URL is strictly client-side. Web browsers never transmit the hash fragment in HTTP requests to web servers, load balancers, or intermediate CDN caches (like Cloudflare or Nginx). View Once stores the 256-bit AES encryption key exclusively inside this URL fragment.
https://viewonce.glofora.com/read/c91a3f0#k7x9L2mP8qR4vW1z...The server only receives
/read/c91a3f0 (the ciphertext pointer). The decryption key following # remains strictly inside the recipient's browser.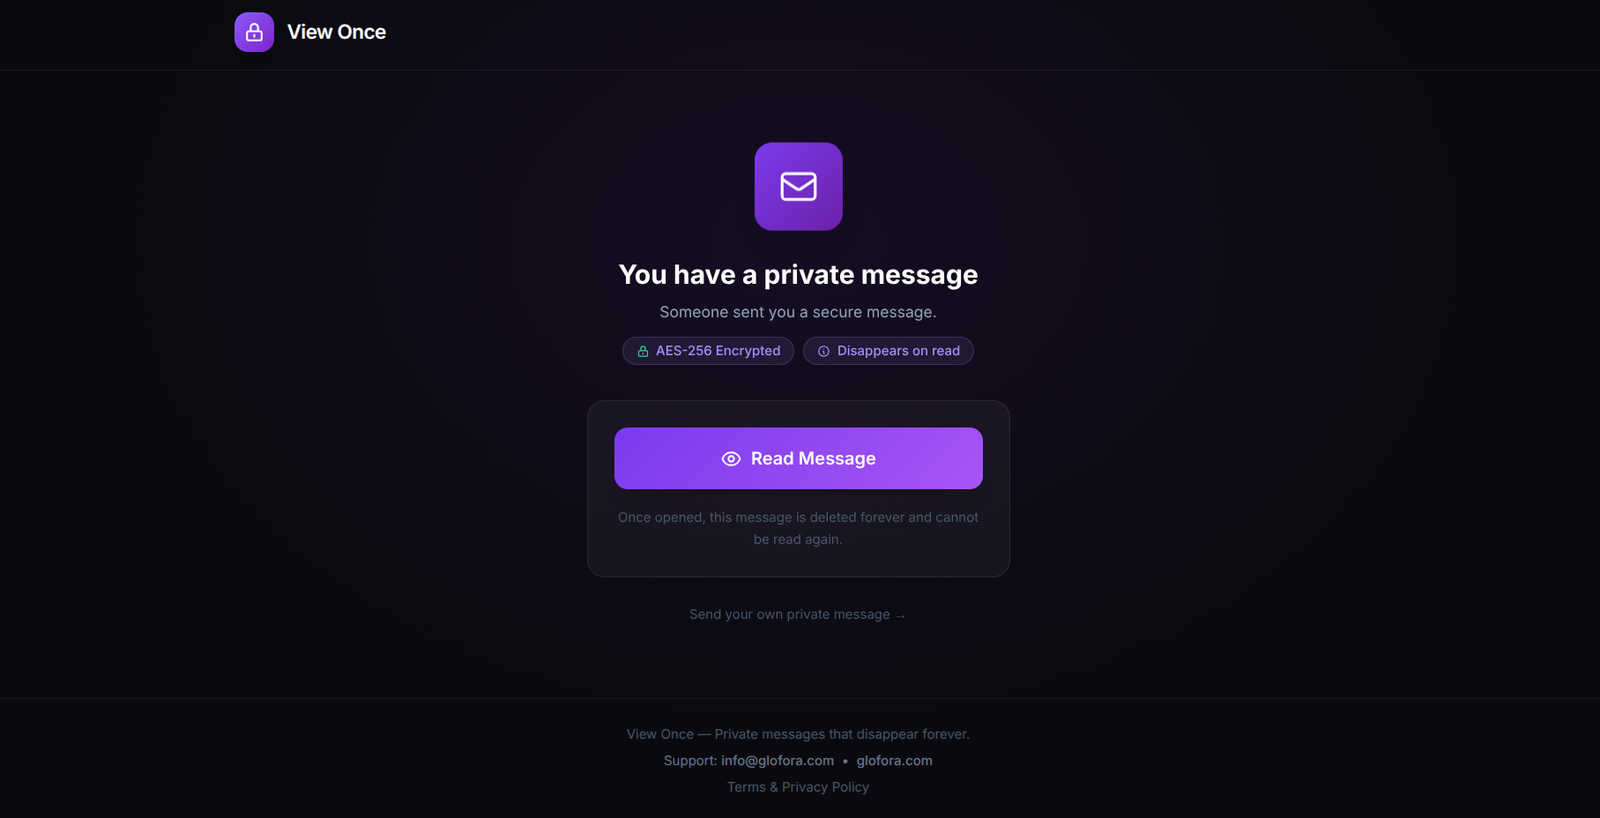
5. Introducing the Encrypted One-Time Reply Channel
A classic dilemma with ephemeral links was the "one-way street" problem: once a recipient read your credentials or reviewed an HD photo, how could they securely respond or send back their own confidential files?
View Once solves this with the Encrypted One-Time Reply feature:
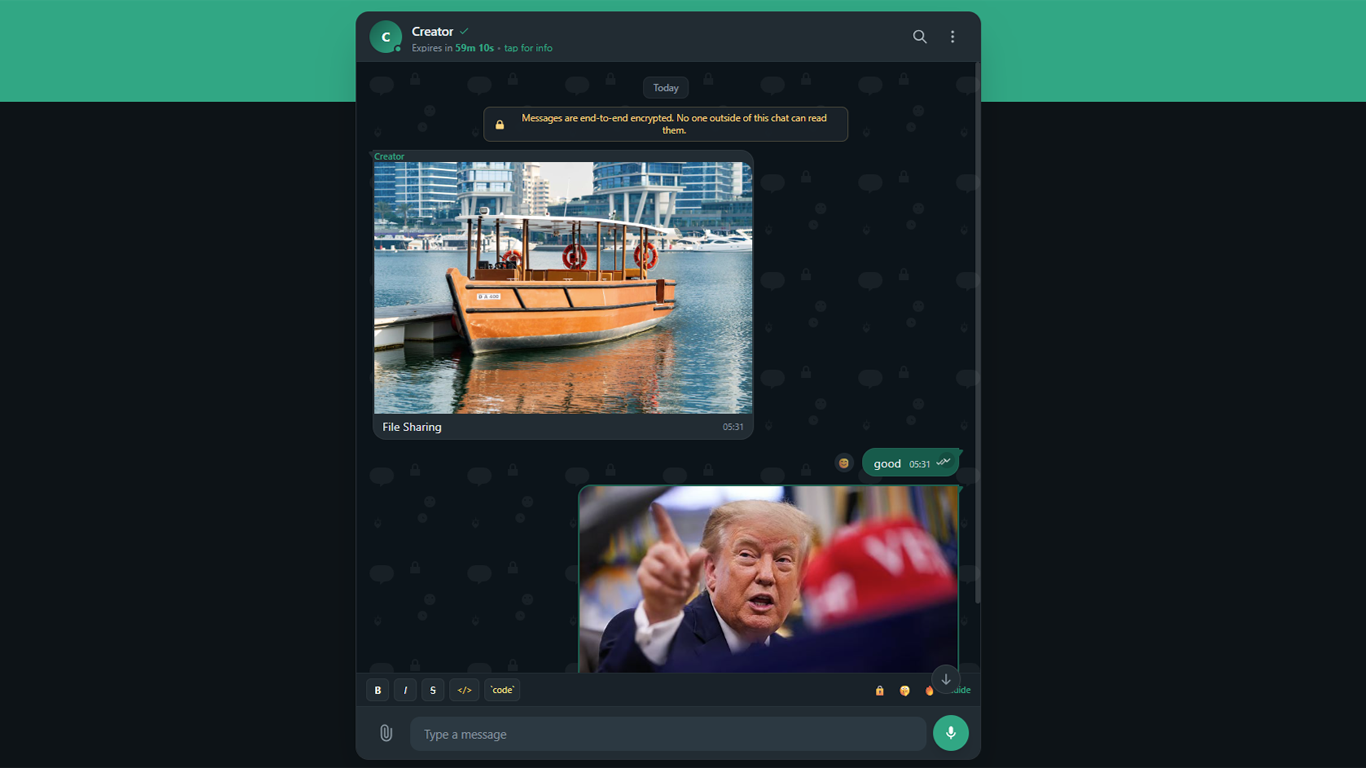
Upon viewing a secret, the recipient is presented with an optional "Reply to this Secret" portal. This initiates a fresh client-side cryptographic session, allowing them to send back their own encrypted note, file attachment, or photo. The reply is bound to an ephemeral token accessible only by the original creator, closing the communication loop with absolute zero-knowledge security.
6. Enterprise & Professional Applications
View Once is deployed across thousands of sensitive daily workflows:
- Software Engineering & DevOps: Safely transferring SSH keys, AWS access tokens, environment variables (
.env), and root database passwords without logging them in Slack or Jira tickets. - Human Resources & Hiring: Requesting prospective employee ID documents, passport scans, tax forms, and compensation offers without storing unencrypted files in email inboxes.
- Legal & Financial Advisory: Transmitting bank account details, wire instructions, draft contracts, and settlement terms with automatic read confirmations.
- Creative & Media Agencies: Sharing watermarked HD previews, unreleased commercial cuts, and confidential design mockups with guaranteed expiration.
Conclusion: Private Sharing Made Frictionless
True digital privacy shouldn't require installing cumbersome software, signing up for accounts, or surrendering personal phone numbers. With support for HD photos, video streaming, universal attachments, and one-time replies, View Once delivers the seamless richness of modern messaging alongside uncompromising zero-knowledge mathematical security.
Ready to protect your confidential communications? Experience View Once for free today — no downloads, no credit card, and zero setup required.